Monitor Vulnerabilities Continuously.
Vulnerabilities don't wait for your next security assessment
Vulnerabilities don't wait for your next security assessment
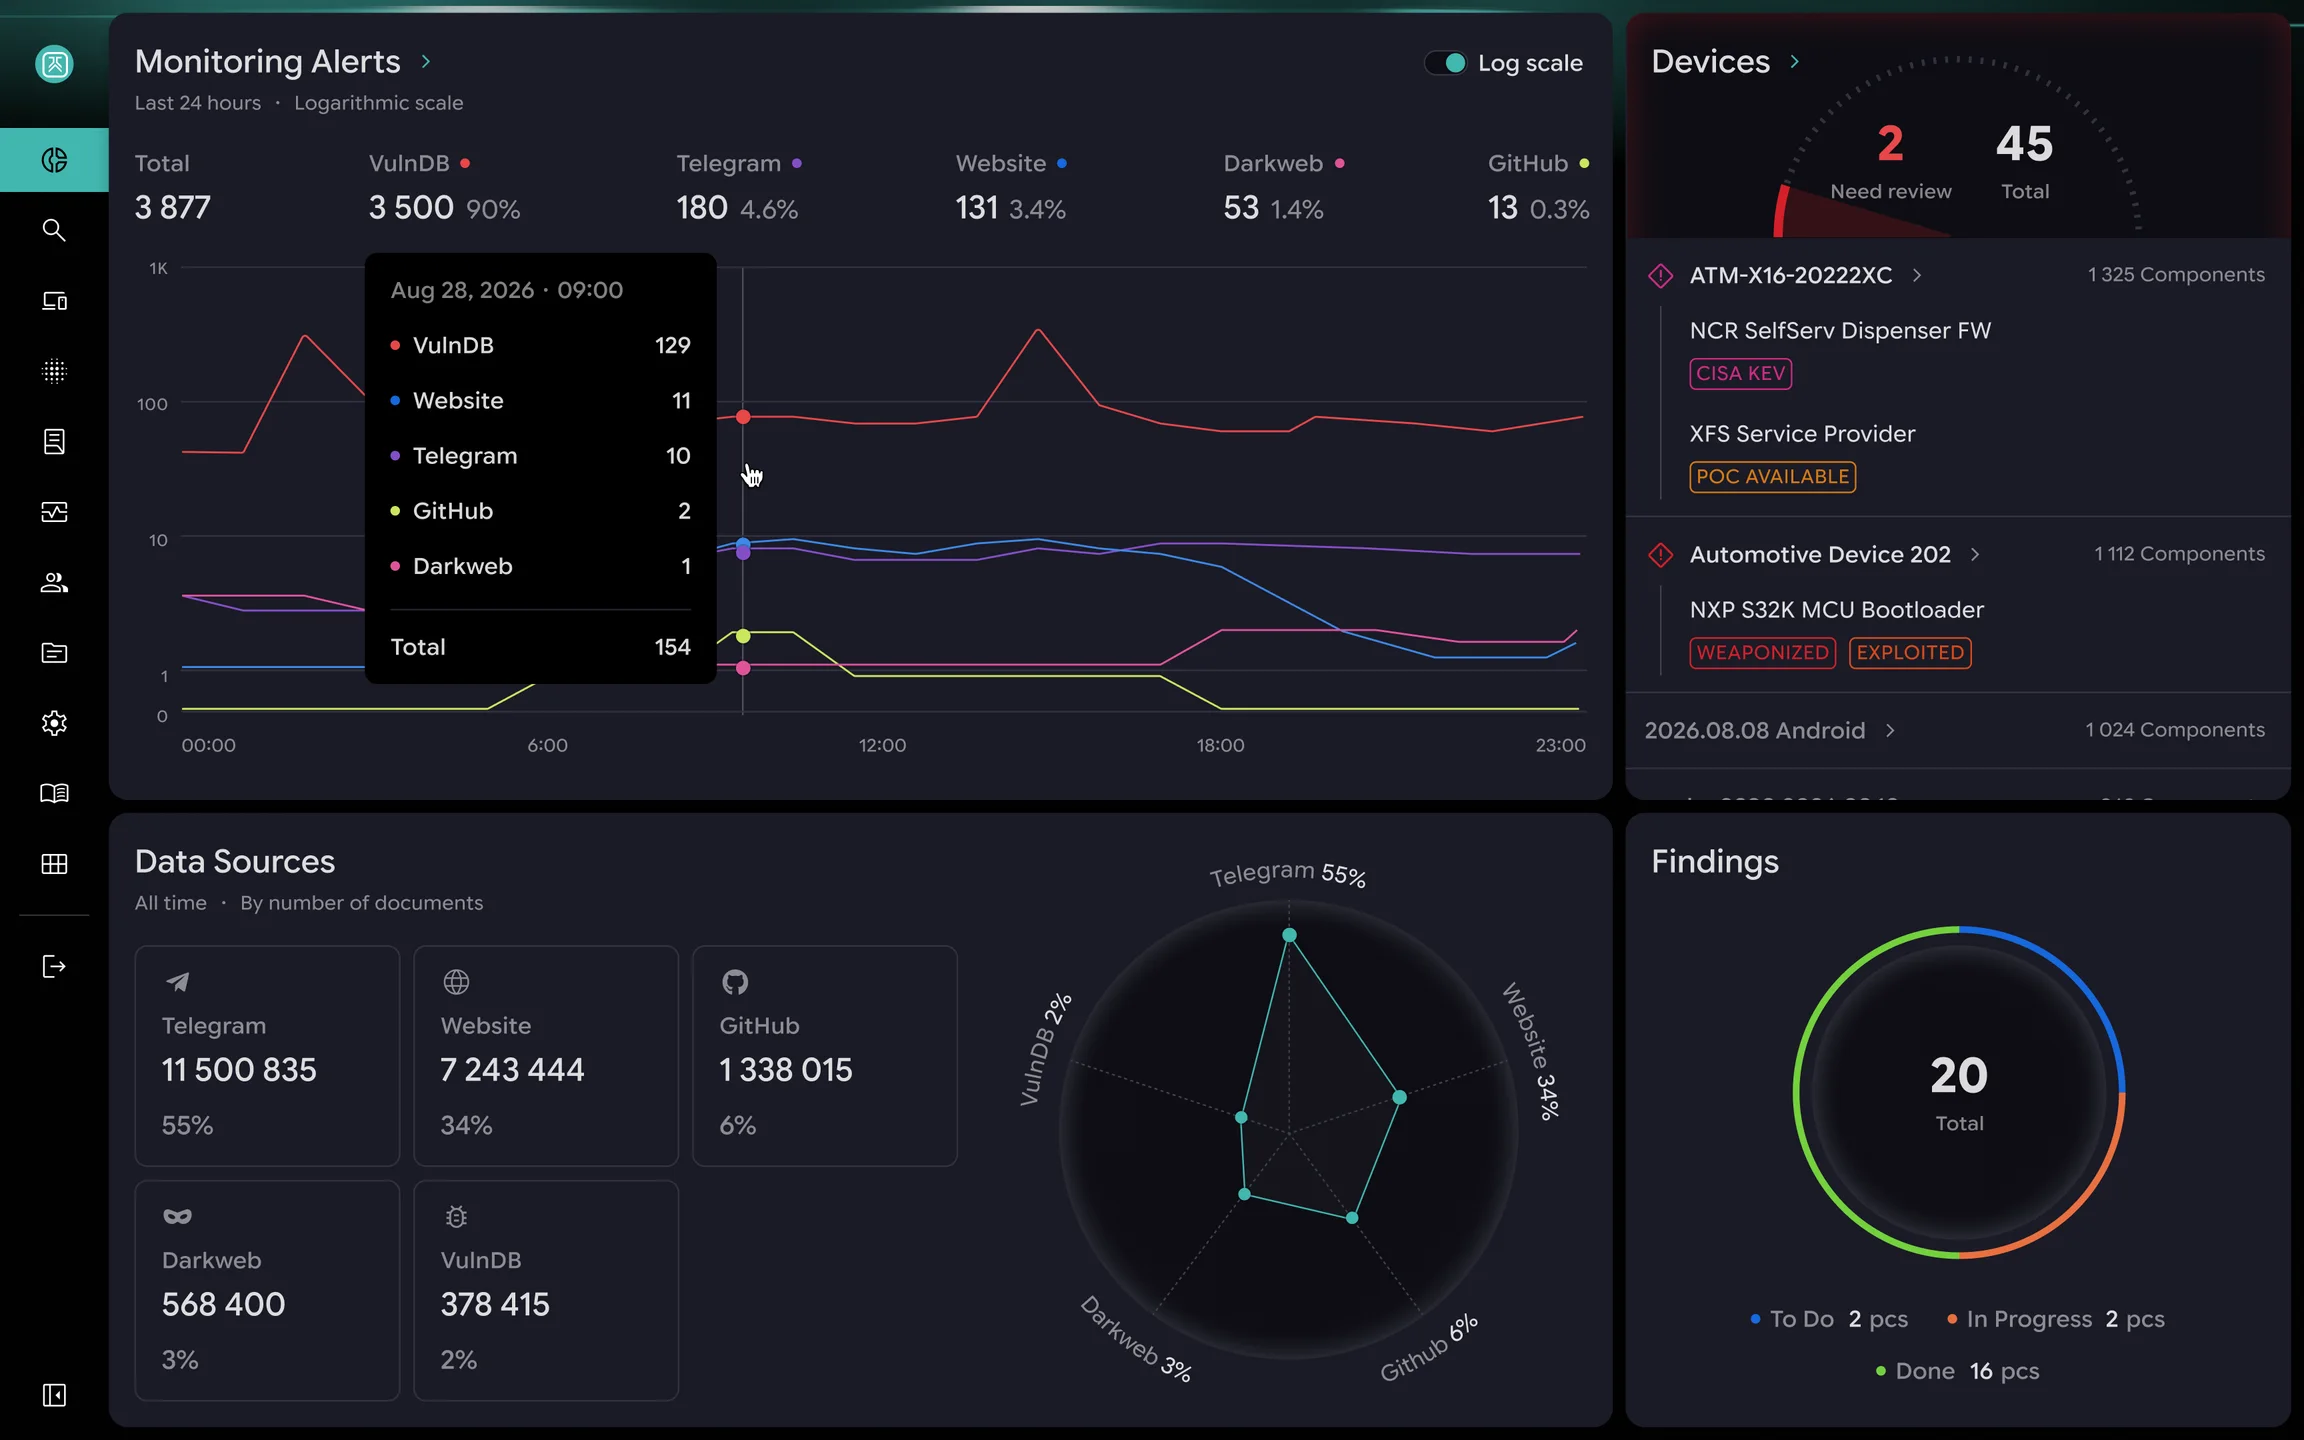
PCA CERVUS combines continuous vulnerability monitoring with threat hunting and web intelligence to help you identify and investigate emerging risks throughout the product lifecycle
From periodic testing to continuous visibility
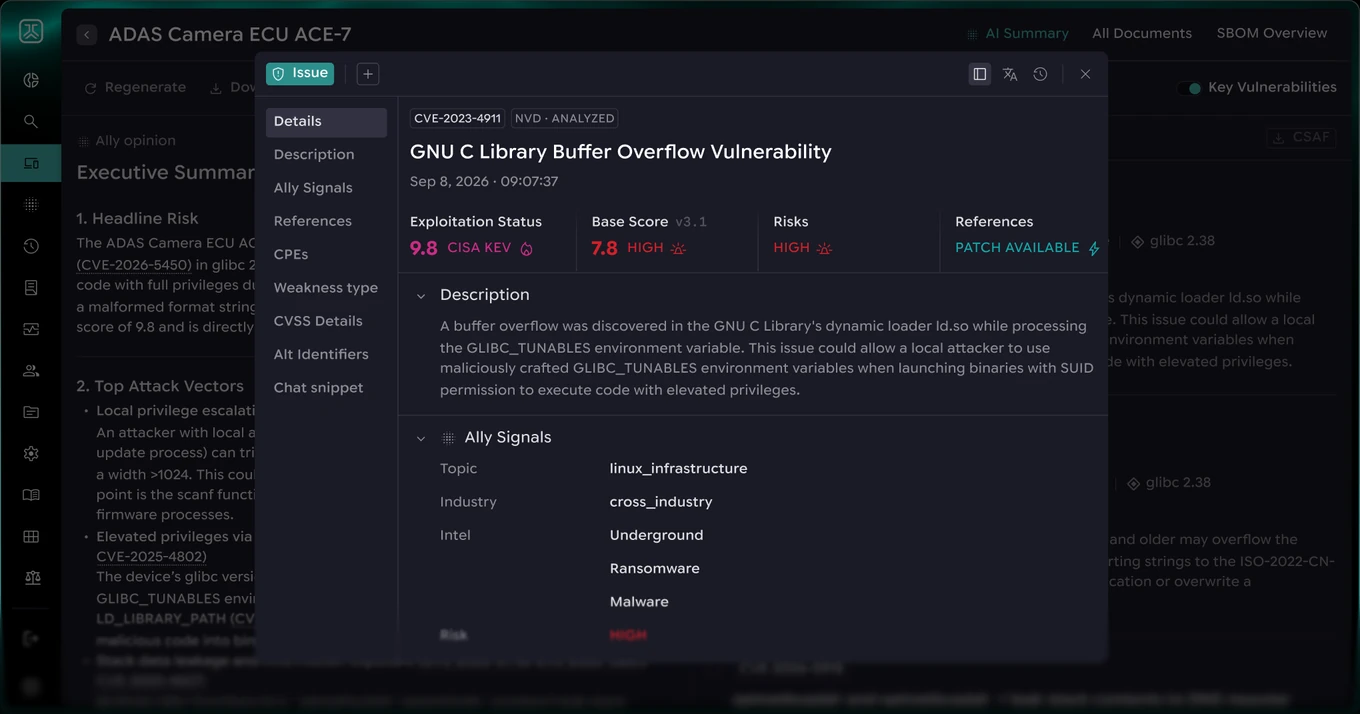
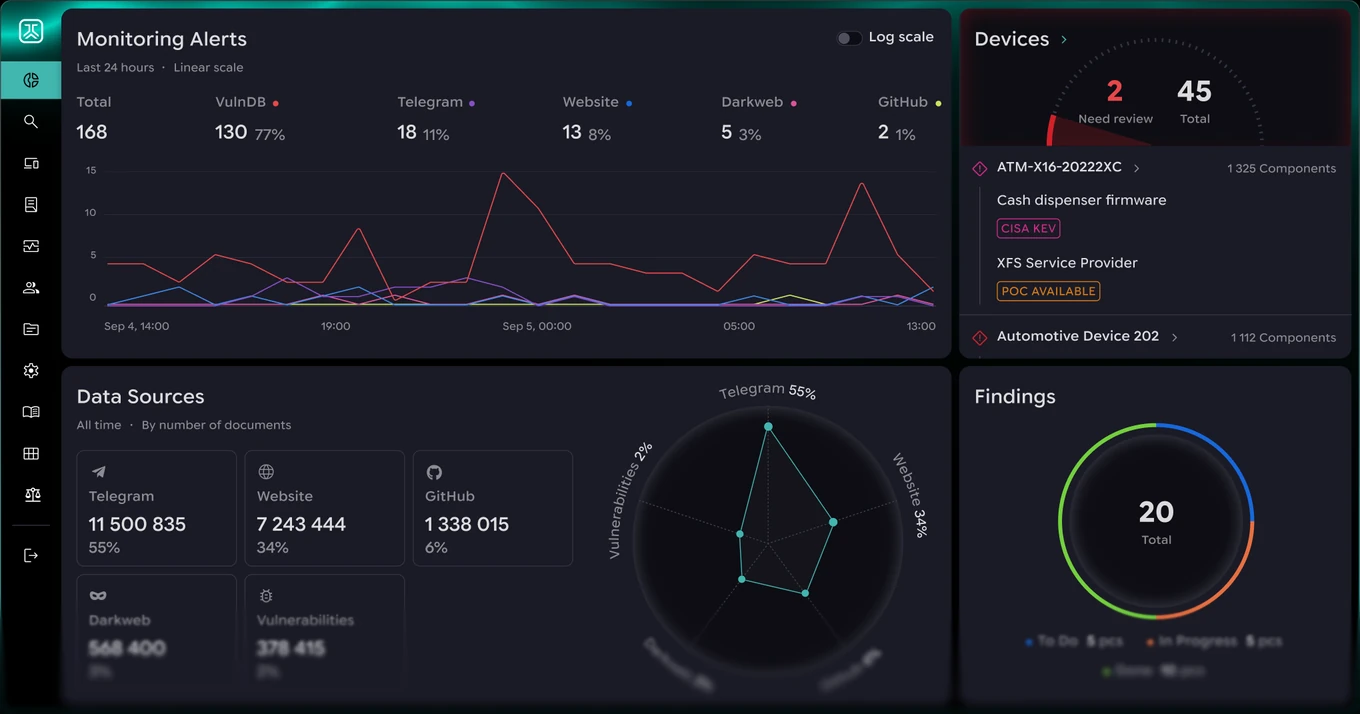
Connect your software inventory or SBOM and continuously monitor vulnerability intelligence relevant to your products and components.
Focus on what matters
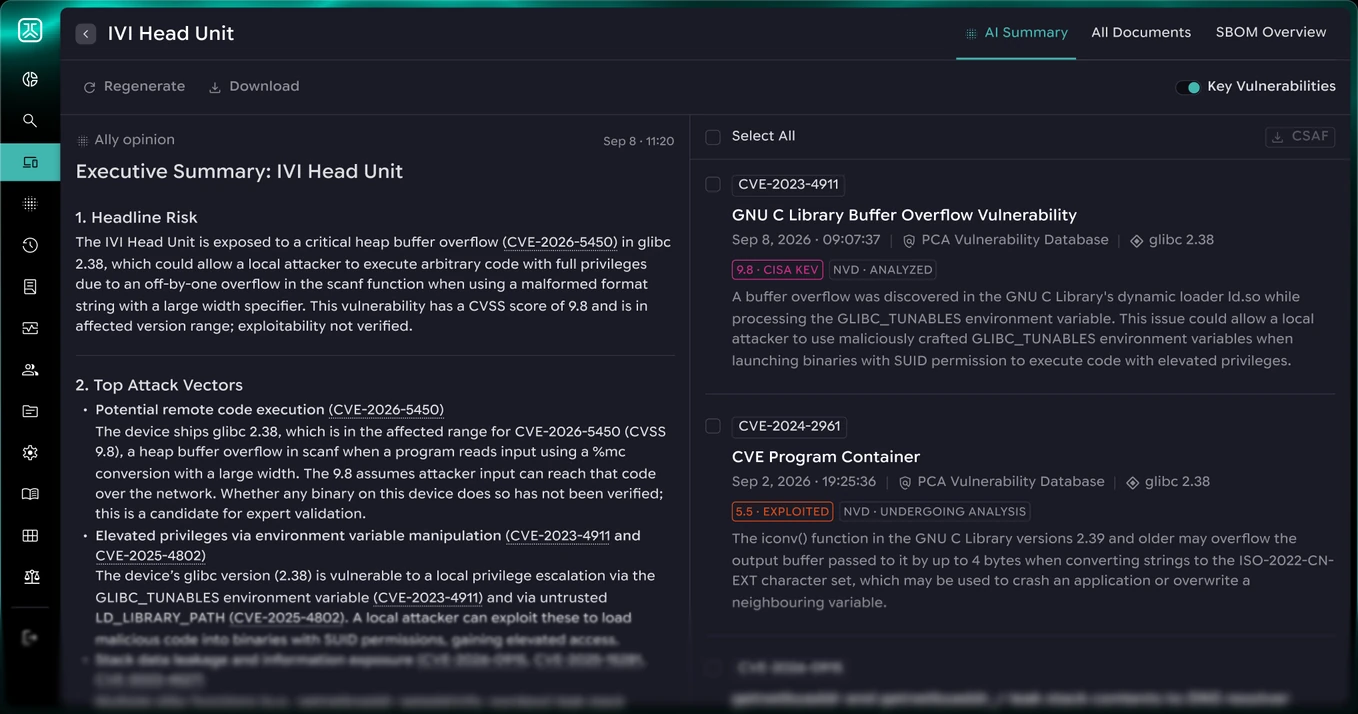
Not every vulnerability affects every product. PCA CERVUS helps identify potentially relevant vulnerabilities and provides the intelligence needed to prioritize investigation and remediation. In-house RAG model, finetuned for threat analysis, helps prioritise and focus your attention on the most critical problems and risks.
Hunt for early signals
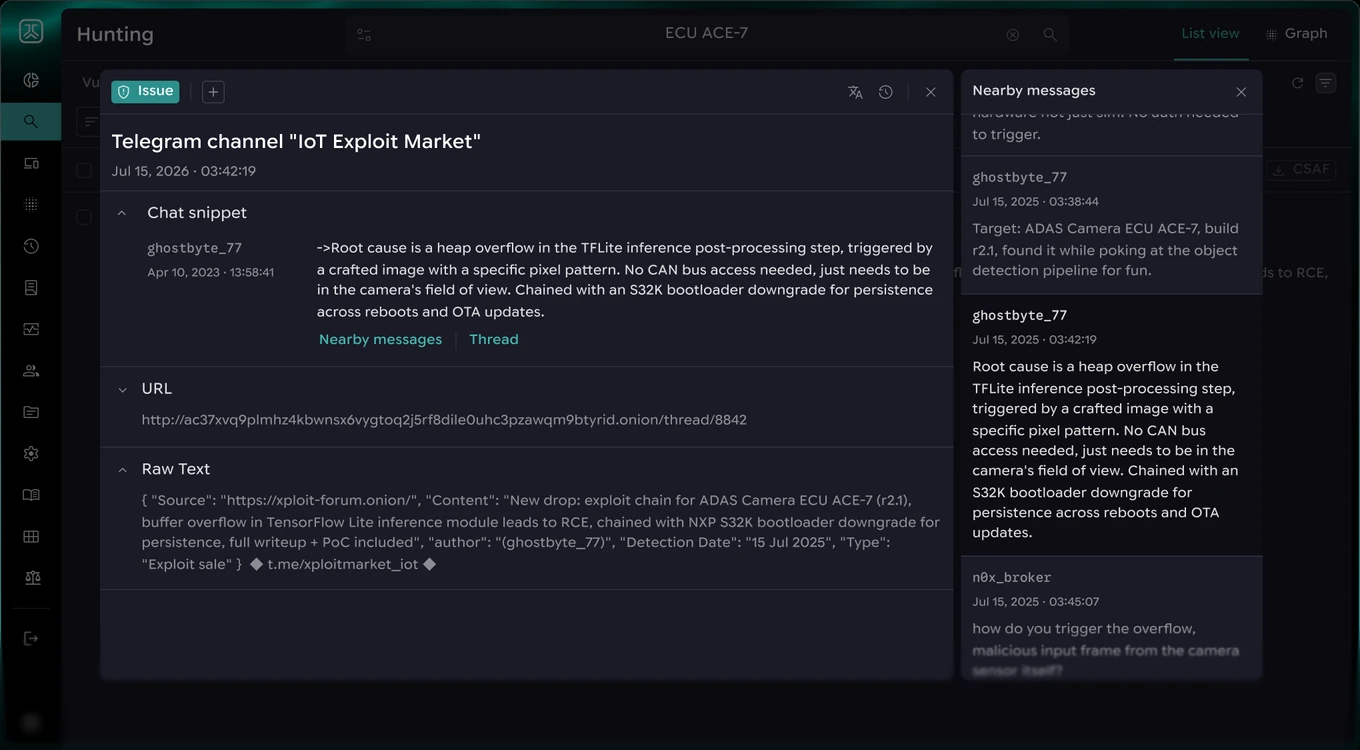
PCA CERVUS threat hunting feature can uncover indicators, discussions and activity that may provide insight into emerging threats before they become widely documented vulnerabilities.
Monitor the deep and dark web
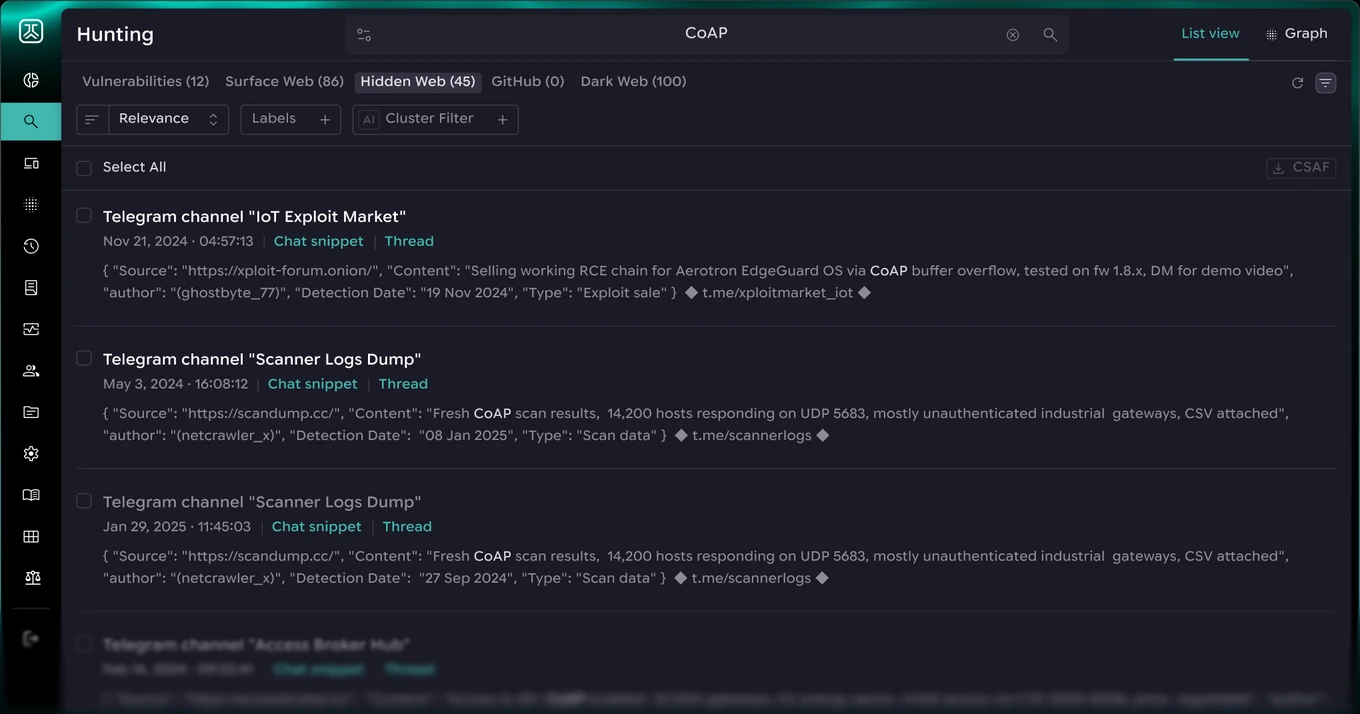
Track relevant activities across the deep and dark web, including discussions, exposed information and other signals that may indicate a developing threat to your products or organization.
Stay ahead throughout the product lifecycle
PCA CERVUS monitors new disclosures, track relevant vulnerabilities and support your teams in validating whether identified issues are present, exploitable or already addressed.