Know what's in your products
Stay ahead of cyber risk

A device-centric vulnerability monitoring and threat intelligence platform for embedded products – from supplier SBOM to remediation evidence – helping you prepare for regulations such as the Cyber Resilience Act (CRA), PCI standards, UNECE R155, and more

Can PCA CERVUS help me?

Get prepared for the Cyber Resilience Act

  • Monitor vulnerabilities continuously
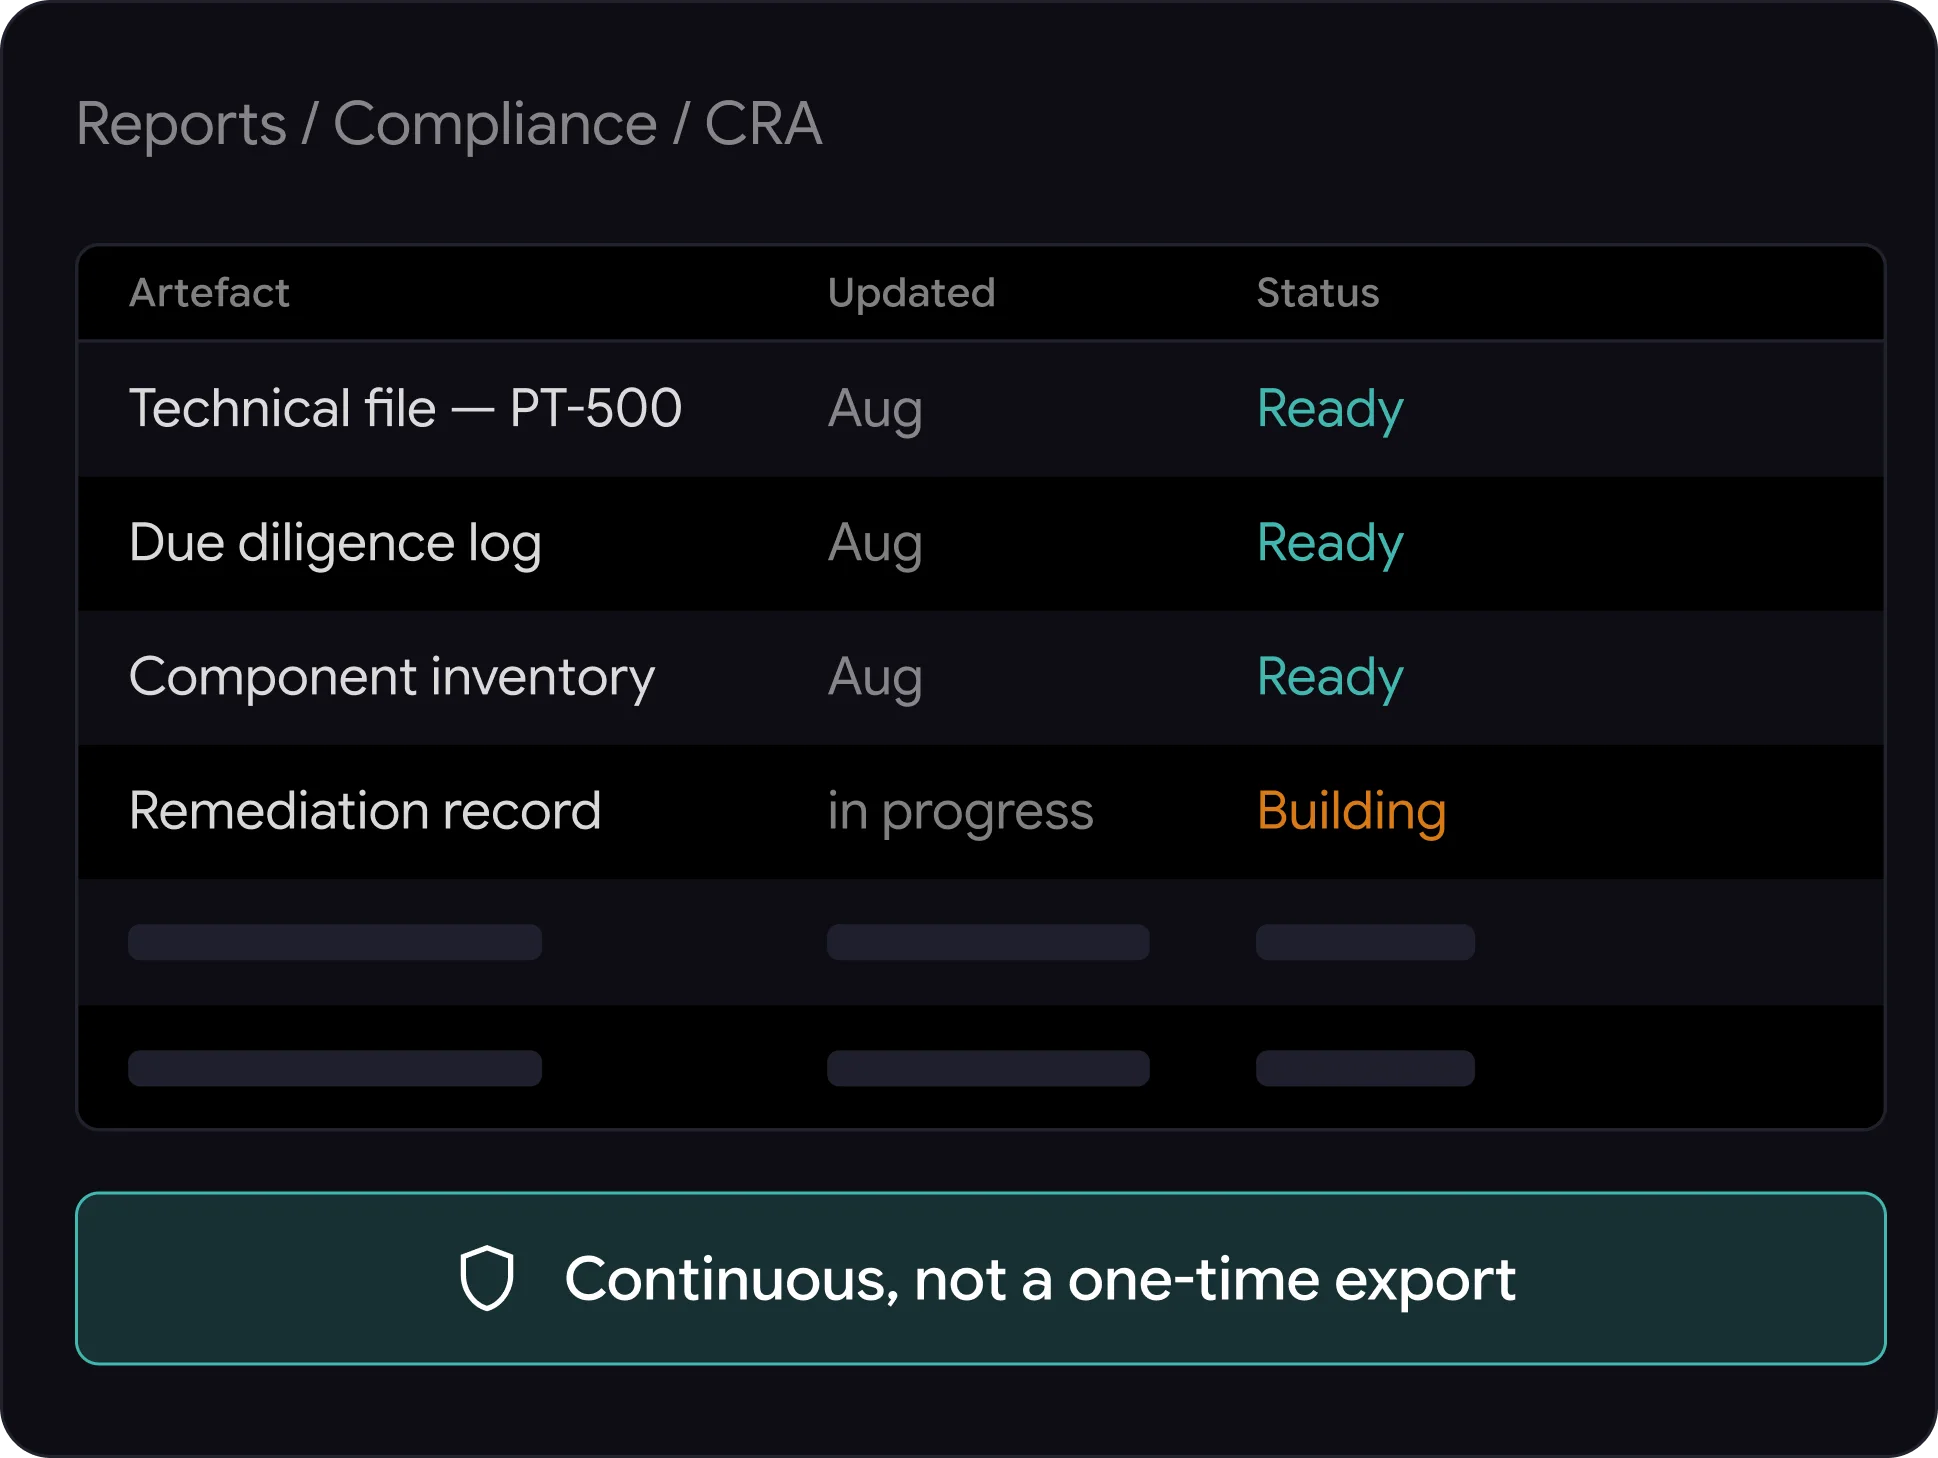
  • Demonstrate due diligence
  • Produce evidence for audits
Get prepared for the Cyber Resilience ActPCA CERVUS compliance reports for the Cyber Resilience Act

From product data
to security decisions

One continuous process across the product lifecycle

Upload SBOM

A supplier SBOM imported into PCA CERVUS
  1. 01 Upload SBOM
  2. 02 PCA CERVUS validates software components
  3. 03 New vulnerabilities detected
  4. 04 Affected products identified
  5. 05 Risk prioritized
  6. 06 Engineering notified
  7. 07 Compliance evidence generated

How can PCA CERVUS
complement traditional TI platforms?

We complement general threat intelligence platforms
and serve a different department inside your organisation
Features
PCA CERVUS
Traditional TI platform
Monitored targets
Embedded Products
General IT assets
Applicable to
Payment, Automotive, Industrial, IoT ecosystem
Mostly IT infrastructure
Alert types
Product related alerts & impact analysis
IT infrastructure related alerts
Basis/focus of threat monitoring
Device components - xBOM as a device model
IOC (Indicator of Compromise)
Focus areas
Device-Centric Supply Chain visibility
Software focused supplier visibility
Risk categories
Product-specific prioritization
IT infrastructure related risk scores
Device centric features – 1 xBOM
SBOM validation & creation
Vulnerability Validation & Patch Verification
Compliance support
PCI PTS Compliance Support
PCI DSS Compliance Support
CRA Compliance Support for Embedded Devices
CRA Compliance Support for Software Products
ISO/SAE 21434 Compliance Support
IEC 62443-4-2 Compliance Support
RED / EN 18031 Compliance Support

Why security teams choose PCA CERVUS

Questions? We have answers

Product security is more than knowing which vulnerabilities exist. It’s about understanding what they mean for your products, your supply chain and your customers. Explore how PCA CERVUS brings product context, device-centric threat intelligence and continuous vulnerability intelligence together to help you make security decisions with confidence.

PCA CERVUS is a device-centric, unified, embedded-focused Vulnerability Monitoring & Threat Intelligence platform that helps product security teams continuously identify device risks, validate and/or generate SBOMs, prioritize vulnerabilities with threat intelligence, and support compliance with evolving regulations such as Cyber Resilience Act, PCI DSS, PCI PTS, RED and UNECE R155.

PCA CERVUS helps organizations continuously discover, assess, prioritize and monitor security risks throughout the product lifecycle – from development and certification through deployment and maintenance.
Trusted by

Securing the world’s top industry players with unmatched cybersecurity expertise.
Discover our proven results with industry leaders.
Explore more case studies

Reduce product cyber risk before
it becomes a product recall