Prepare for the Cyber Resilience Act and more. Turn CRA requirements into an ongoing product security process
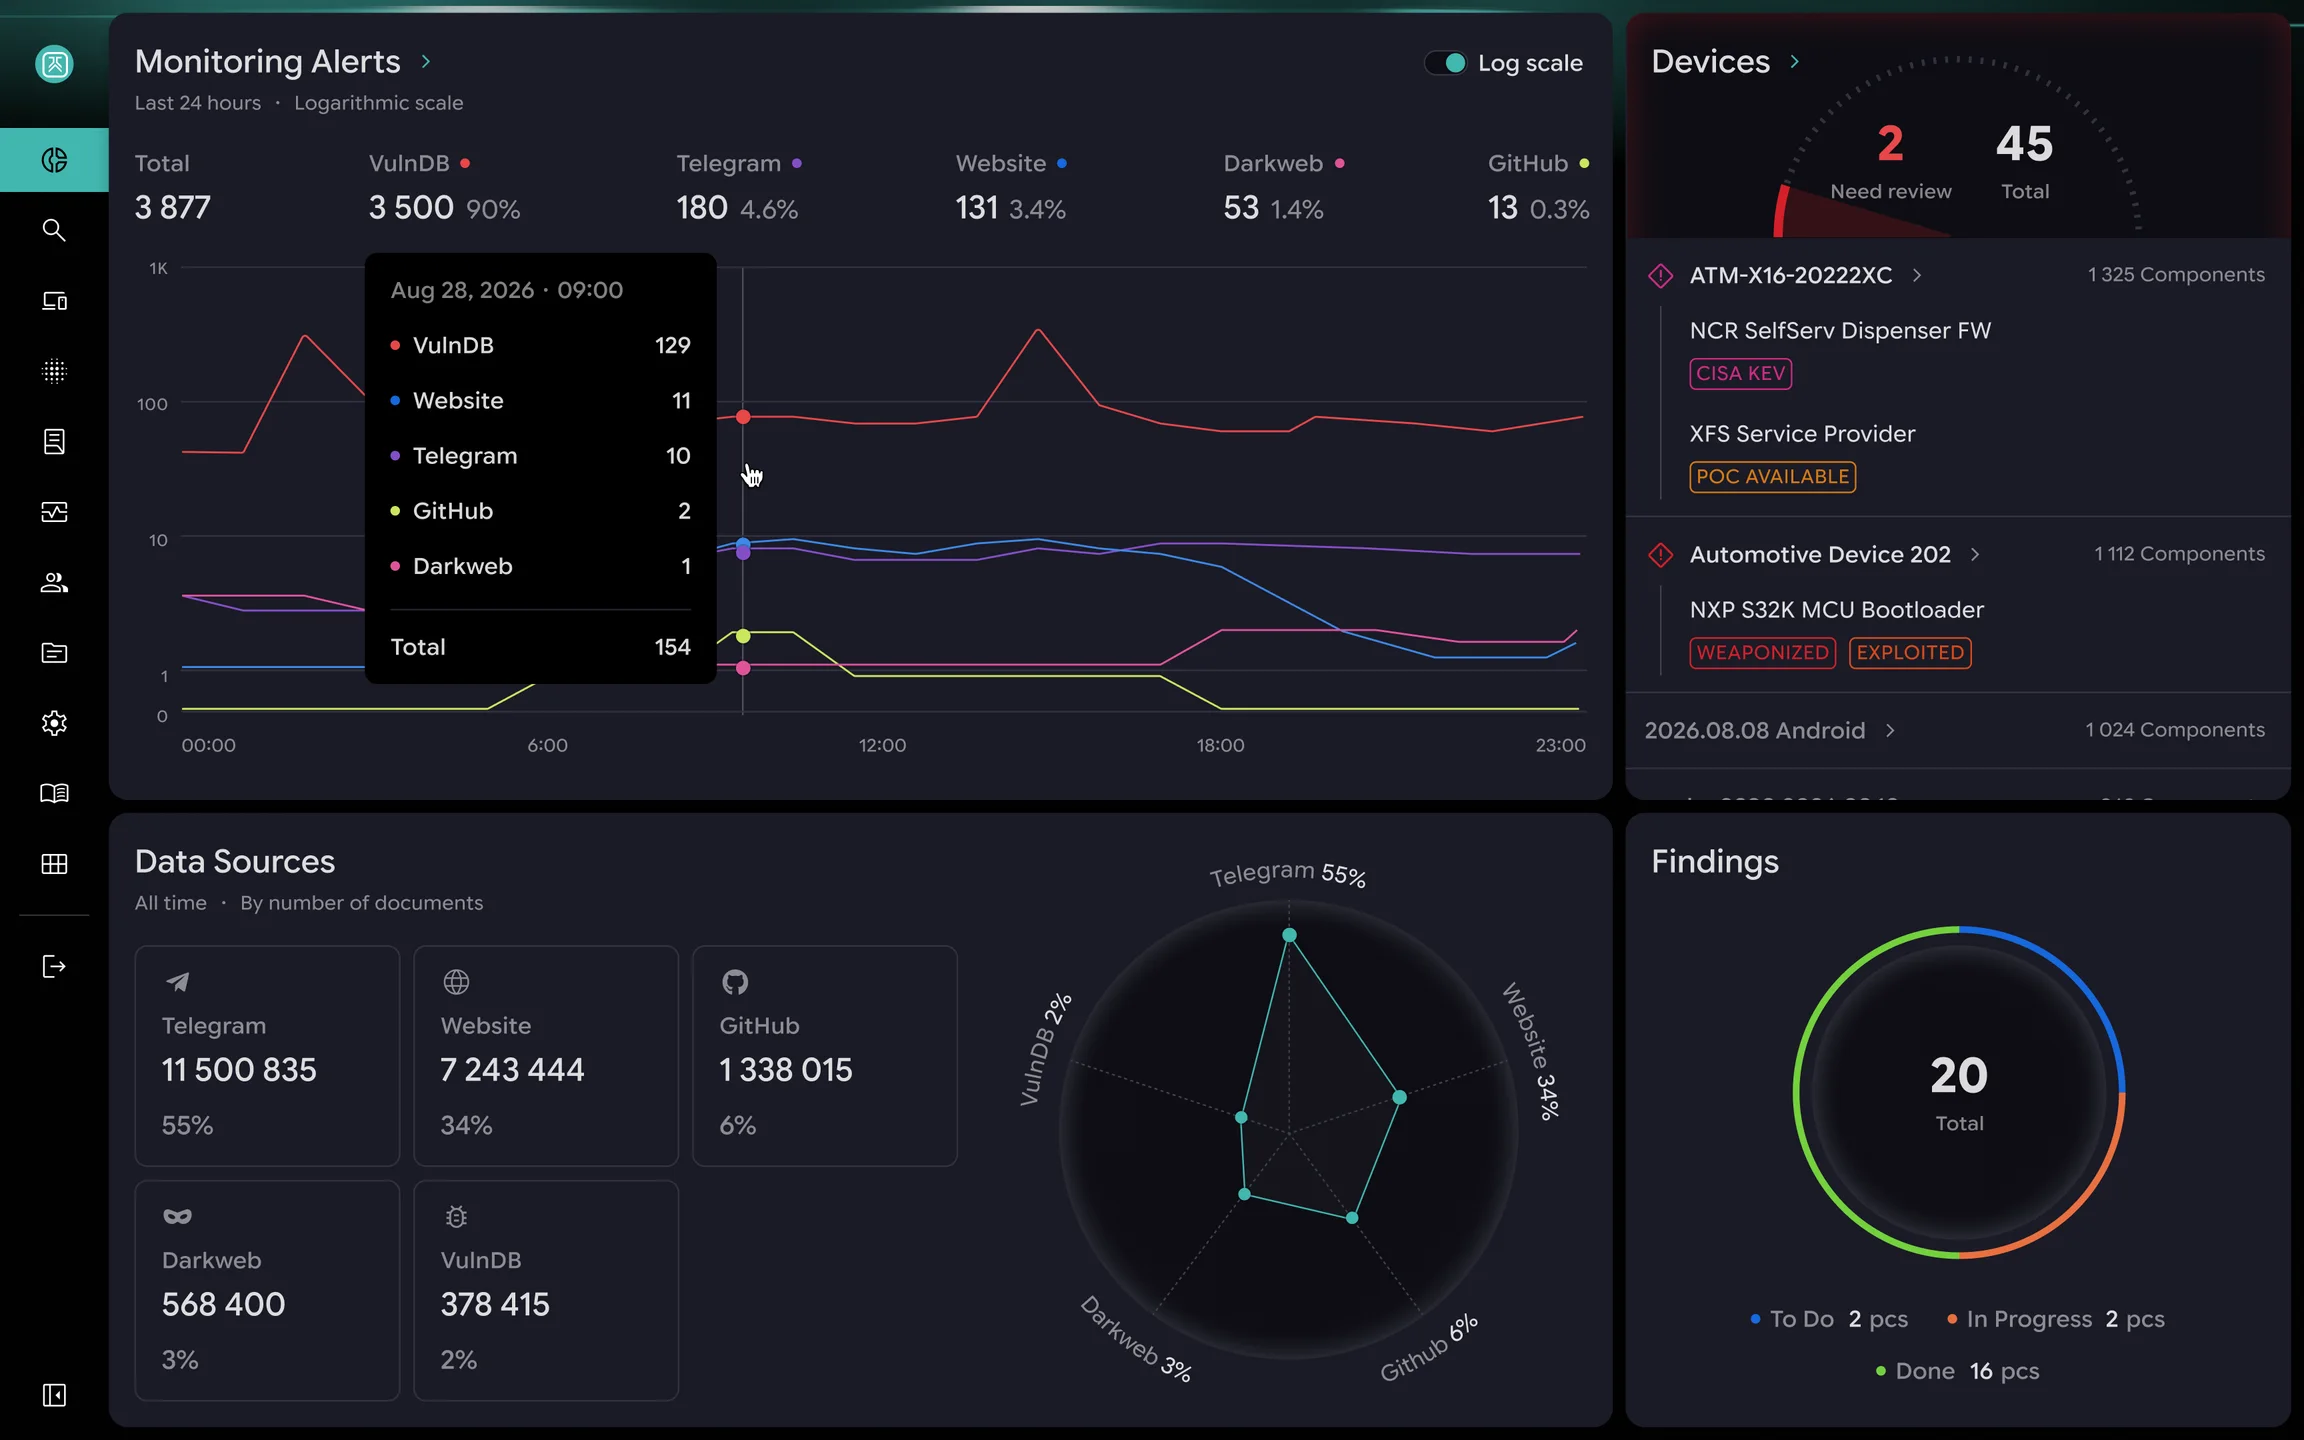
PCA CERVUS brings vulnerability intelligence, threat hunting, OSINT and dark web monitoring together to help product security teams maintain continuous visibility into the security posture of your embedded products
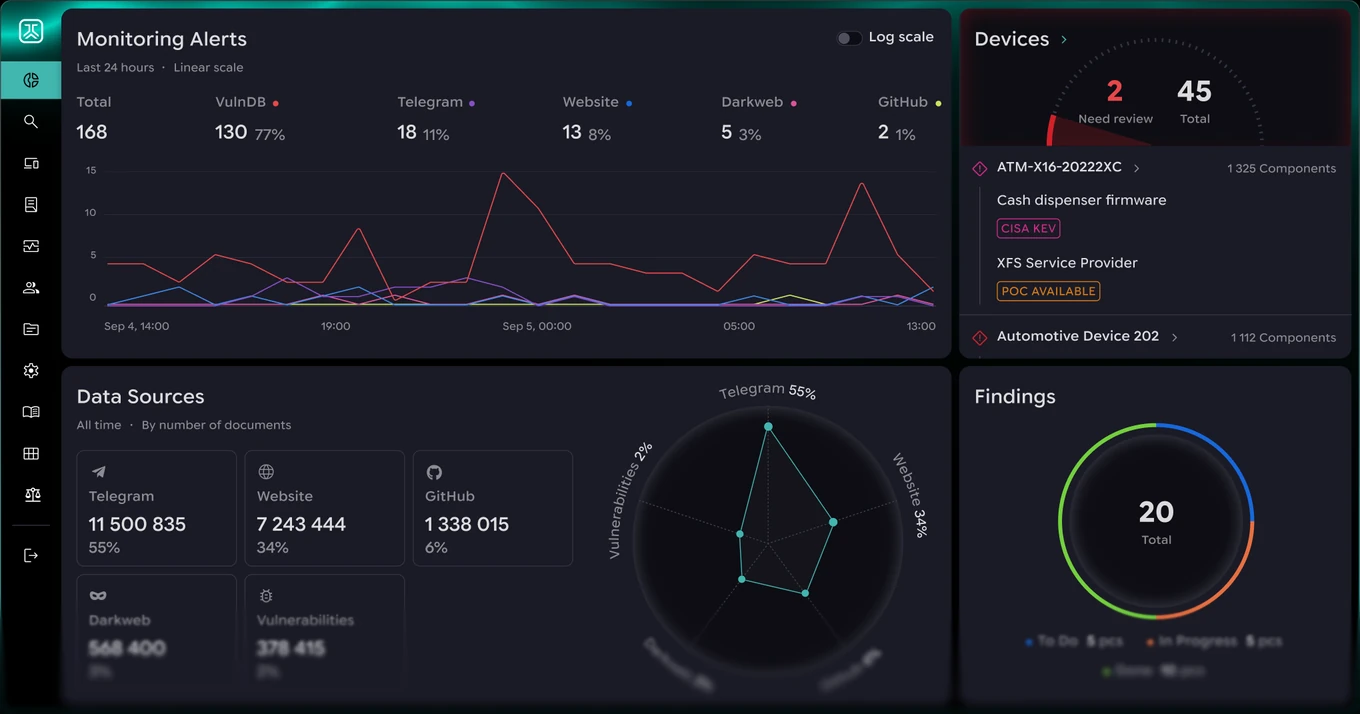
Monitor vulnerabilities that matter
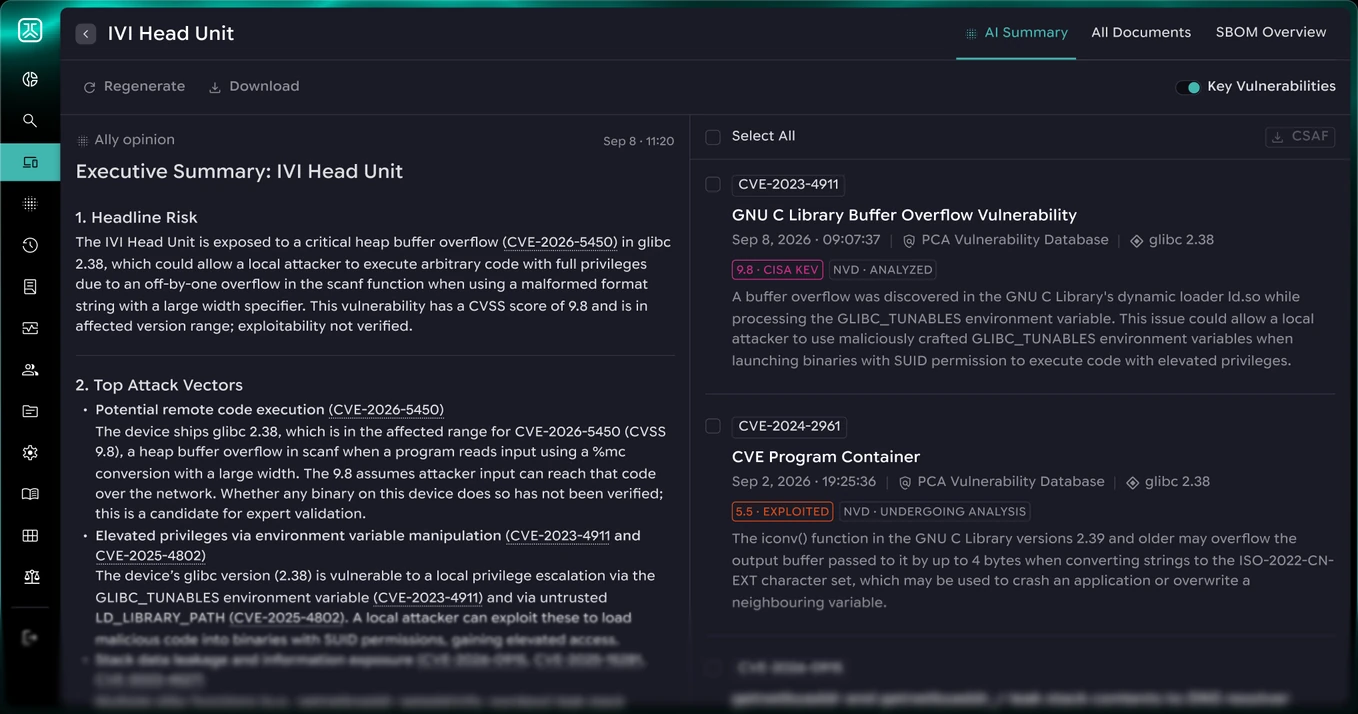
PCA CERVUS continuously monitors vulnerabilities and automatically assess relevance and applicability to software and hardware components of your embedded devices. Go beyond CVE feeds with PCA's embedded security expertise to investigate whether vulnerabilities are actually relevant to your products.
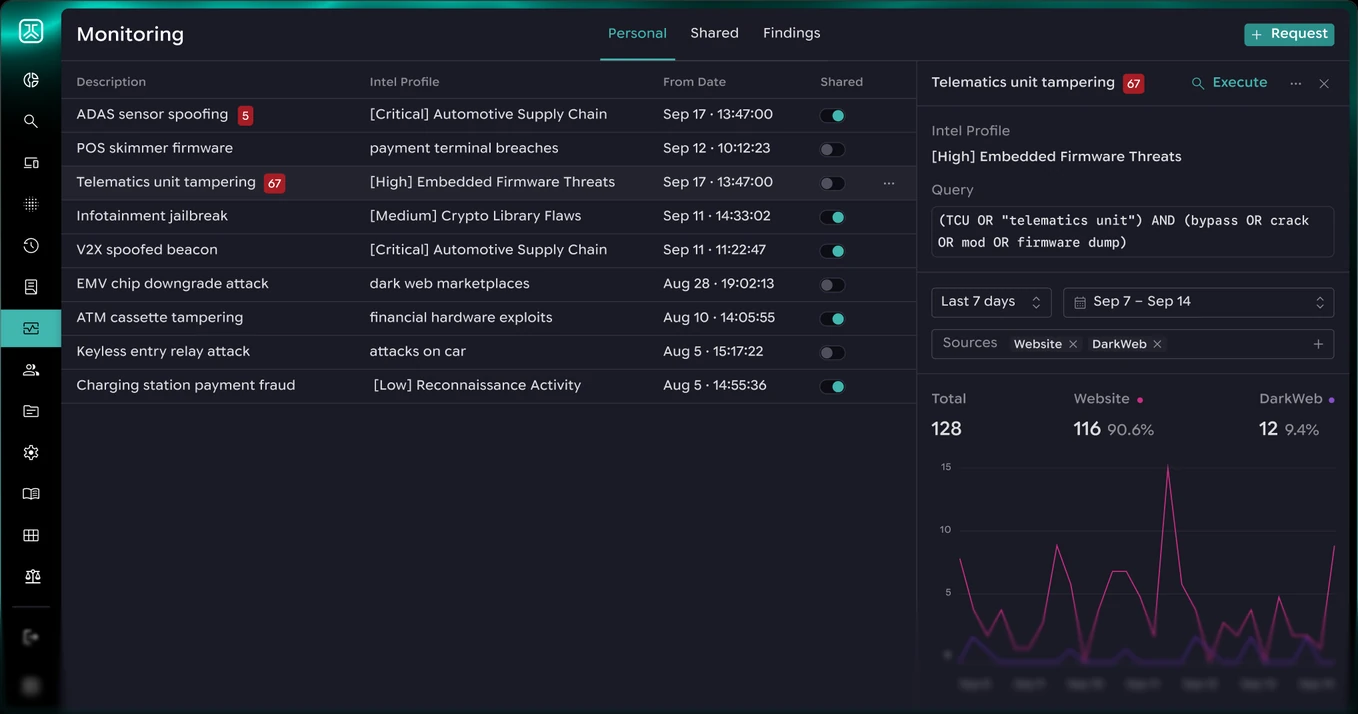
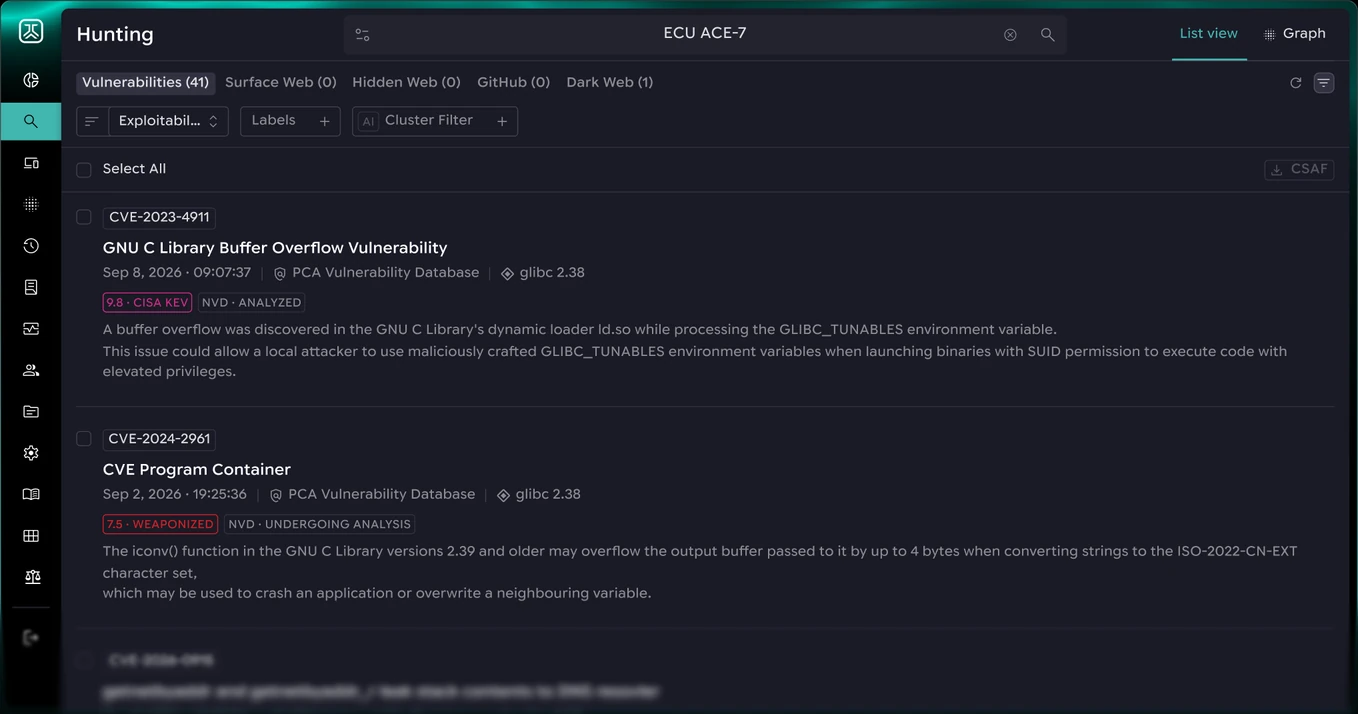
Hunt for emerging threats
PCA CERVUS supported by our threat intelligence analysts actively investigate emerging threats, exploit activity and attacker tooling, techniques and grey-market sales that may not yet be fully reflected in conventional vulnerability databases.
Support your vulnerability management process
Combine automated vulnerability intelligence with PCA's embedded cybersecurity expertise to investigate vulnerabilities, assess their relevance and track remediation via our Vulnerability Validation & Patch Verification flow.
Vulnerability Validation
& Patch Verification Flow
& Patch Verification Flow
Input
CVEfrom PCA CERVUSTarget binaryOrchestrator & subagents
AGENTPatch & source finderSUBAGENTFunction locator for stripped binariesSUBAGENTVulnerability validatorPF detectorAgentic analysis
MCPLLMAgentOPTIONALReversing toolsAPIPCA CERVUS APIVerdict
PATCHED?YESVulnerability patchedNOStill vulnerable
Build a stronger foundation for CRA compliance
PCA CERVUS supports the continuous monitoring and vulnerability management activities that form an important part of product cybersecurity under the CRA - helping you move from periodic checks to an ongoing security process.